For Security Leaders
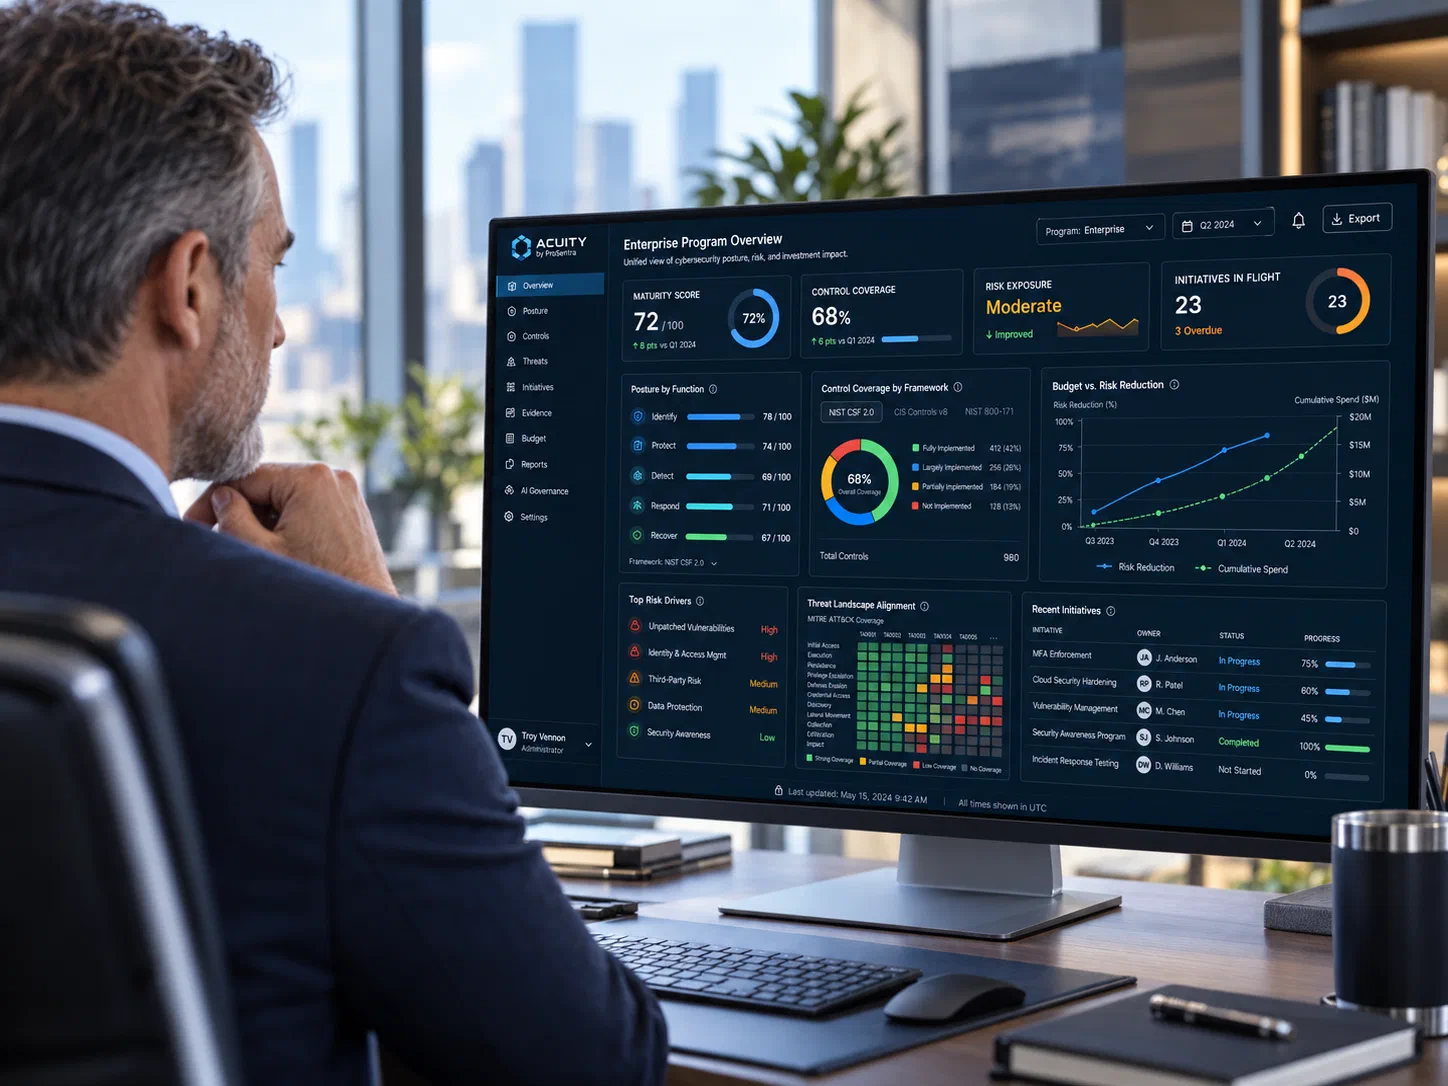
See your entire program at once
Your controls live in one spreadsheet, your tools in another, your threat picture in a slide deck and your budget somewhere else. Acuity connects them, so you can see what reduces risk, what it costs, and what to do next, without rebuilding the picture before every board meeting.
- Controls, threats, tools, people and budget in one system
- Priorities weighted by the threat groups that target your industry
- Spend versus outcomes, in numbers the board understands
- Progress measured against a baseline, not a feeling
The Challenge
You can't run a program you can't see
Five sources, no single picture
Assessments, tool inventories, threat intel, staffing and budget are tracked separately, so every decision starts with reconciling them.
Assessments that go stale
The annual assessment is out of date the week it's delivered, and nothing ties it to the work that follows.
Budgets defended with activity
Leadership asks what the money bought. Task lists and ticket counts don't answer that.
The Acuity Approach
Connect the data, then run the program from it
1. Know where you stand
Score your controls against NIST CSF 2.0 or CIS Controls v8.1, backed by your own evidence, and see technique-level MITRE ATT&CK coverage across your tools and controls.
2. Prioritize what reduces risk
Priorities are weighted by the threat groups that target your industry. See where tools overlap, where coverage is thin, and what the budget should buy.
3. Execute and prove it
Recommendations become initiatives and tasks with evidence. Every plan is measured against a frozen baseline, so progress is exact and the Acuity Score tells the story in one number.
- 691
- MITRE ATT&CK techniques mapped across 34 security tool types
- ~8,000
- Mappings between NIST CSF 2.0 subcategories and ATT&CK techniques
- 25
- Real adversary emulation scenarios replayed against your posture
Frequently asked questions
Is Acuity a GRC tool?
No. GRC tools track compliance. Acuity runs the security program: it connects maturity, threat coverage, tools, people and budget, and shows what to do next and what it’s worth.
Are the scores generated by AI?
No. Scores, coverage, costs and priorities are computed the same way every time, so results are repeatable and explainable. AI writes the narratives and cites the evidence behind them.
Where should I start: Essentials or Core?
Start with Acuity Essentials if you need an evidence-backed baseline, gaps and a roadmap. Move to Acuity Core when you want to run the whole program continuously, with spend versus outcomes, staffing and the Acuity Score.
Which frameworks do you support?
NIST CSF 2.0, CIS Controls v8.1 and NIST 800-171 (CMMC 2.0), mapped to MITRE ATT&CK.
Does it work with how my team already tracks work?
Recommendations become objectives, initiatives and tasks inside Acuity, and initiatives and tasks sync two-way with Smartsheet.
See your program in one view
Talk with the security leaders who built Acuity about where your program is today and what the whole picture would show you.