Acuity Essentials
An evidence-backed cybersecurity maturity assessment
Know where you stand and what to fix next. Acuity Essentials assesses your security controls against the NIST Cybersecurity Framework (CSF 2.0), CIS Controls v8.1, or NIST 800-171 (CMMC 2.0), shows where your controls and tools leave gaps against the threats that target your industry, and builds a prioritized cybersecurity roadmap — without standing up a full operating model on day one. AI Governance inventories your AI systems against the NIST AI RMF.


Framework assessments
A structured, current view of your cybersecurity maturity and a practical path forward. Acuity Essentials runs guided assessments against the NIST Cybersecurity Framework (CSF 2.0), CIS Controls v8.1 with Implementation Group mapping (IG1–IG3), or NIST 800-171 (CMMC 2.0). Assess the way that suits your team: answer guided questions, upload your policies and evidence for Acuity's AI to draft the assessment, or record a completed one. Acuity checks every answer against your evidence and scores each CSF 2.0 subcategory on a 1–5 maturity scale, with a rationale and how close you are to the next level.
- Guided maturity assessment with clear maturity and Acuity scores
- Gap identification at the control level
- Prioritized recommendations from controls mapped to threats
- A practical, ready-to-implement roadmap
- Documents-first assessments: Acuity's AI drafts answers from your policies
- Evidence-checked answers with targeted follow-up questions
- NIST 800-171 (CMMC 2.0) assessments
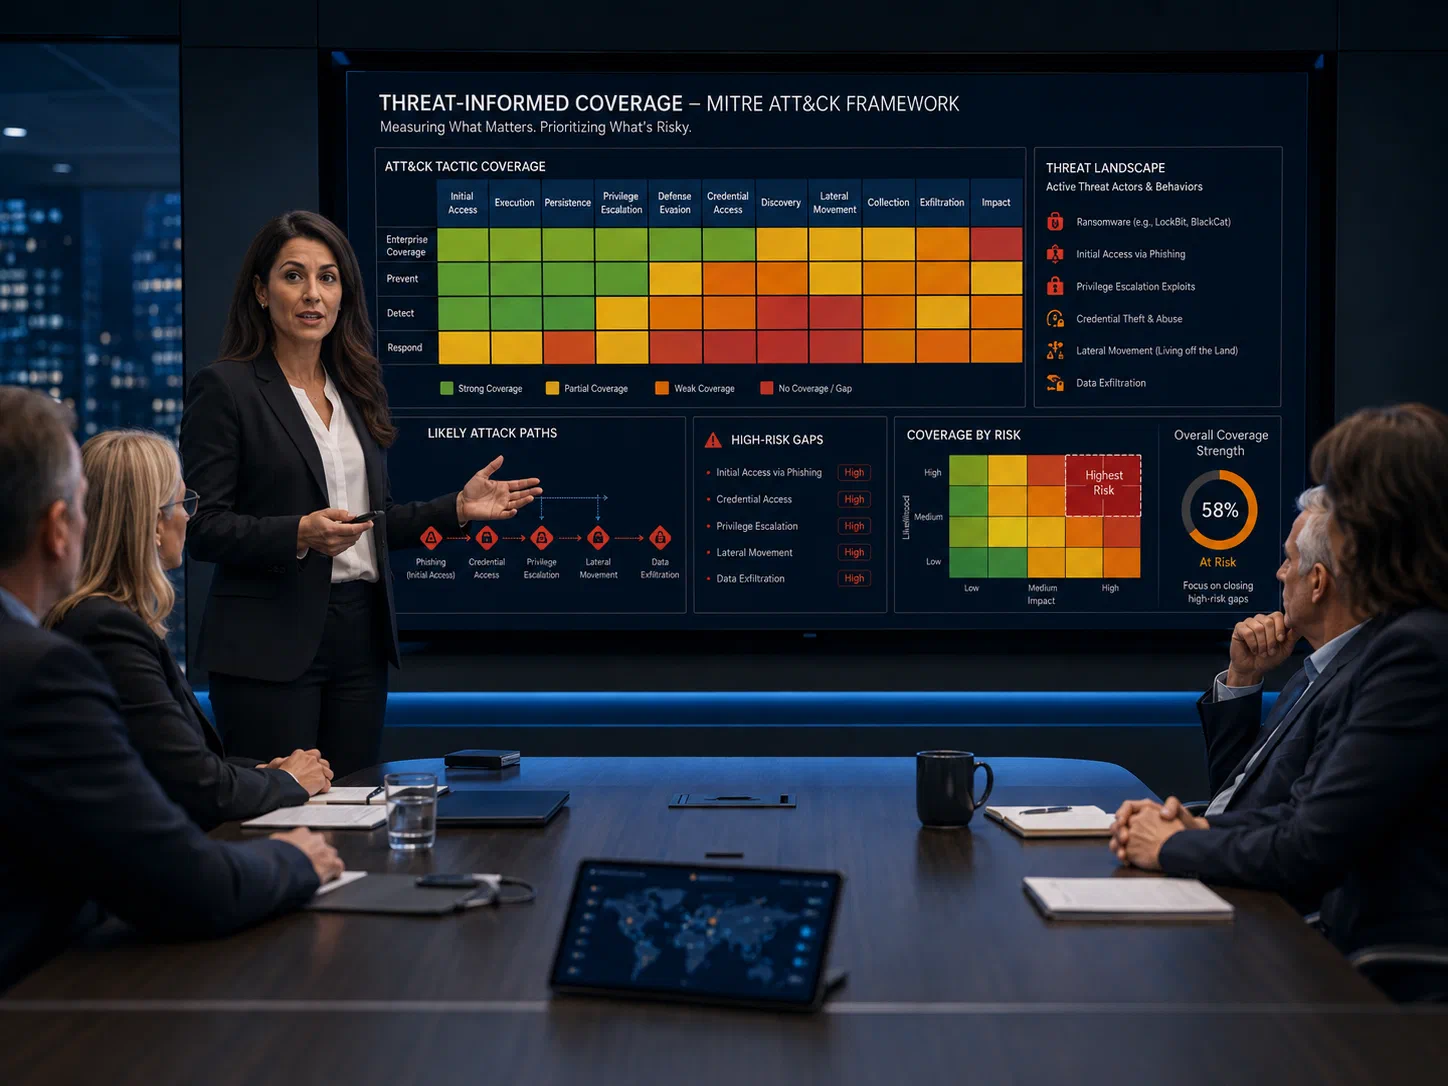
Threat coverage and gap analysis
Maturity scores alone don't tell you whether you're protected against the attacks that matter. Acuity Essentials shows how well your security controls and tools cover the MITRE ATT&CK techniques used by the threat groups that target your industry, across the attack lifecycle. It then finds your gaps in three views and turns them into a prioritized cybersecurity roadmap with an executive summary.
- Industry-weighted MITRE ATT&CK threat coverage
- Tool gaps: the missing tool types that would add the most coverage
- Maturity gaps: controls below targets pre-filled from industry benchmarks
- Policy gaps: AI review of your documents against a 36-item evidence checklist
- AI roadmaps linked back to the gaps they close

AI Governance
AI is moving faster than most security programs, and most are still handling it ad hoc. AI Governance helps you inventory AI systems, understand the risks they carry, apply appropriate controls and policies, and maintain ongoing oversight using the NIST AI Risk Management Framework. Pair it with our AI governance policy service for hands-on help.
- AI system inventory and classification
- Risk assessment aligned to the NIST AI RMF
- Policy and control guidance
- Ongoing monitoring and evidence support
Why Essentials
A lower-friction way in
Fast to value
A clean baseline and clear control-level priorities, ready for the next budget conversation.
Framework-aligned
The NIST Cybersecurity Framework (CSF 2.0), CIS Controls v8.1, and NIST 800-171 (CMMC 2.0) for security; the NIST AI RMF for AI risk.
Upgrades to Core
Same scoring model, so moving to the full operating system does not mean starting over.
Evidence-backed
Acuity's AI cites the evidence behind its findings, and nothing is scored on a claim your documents don't support.
Threat-informed
Priorities are weighted by the threat groups that actually target your industry, not a generic top-ten list.
Built for advisors
vCISOs, MSPs and security advisors can assess many clients from one platform, each isolated, with a client portal.