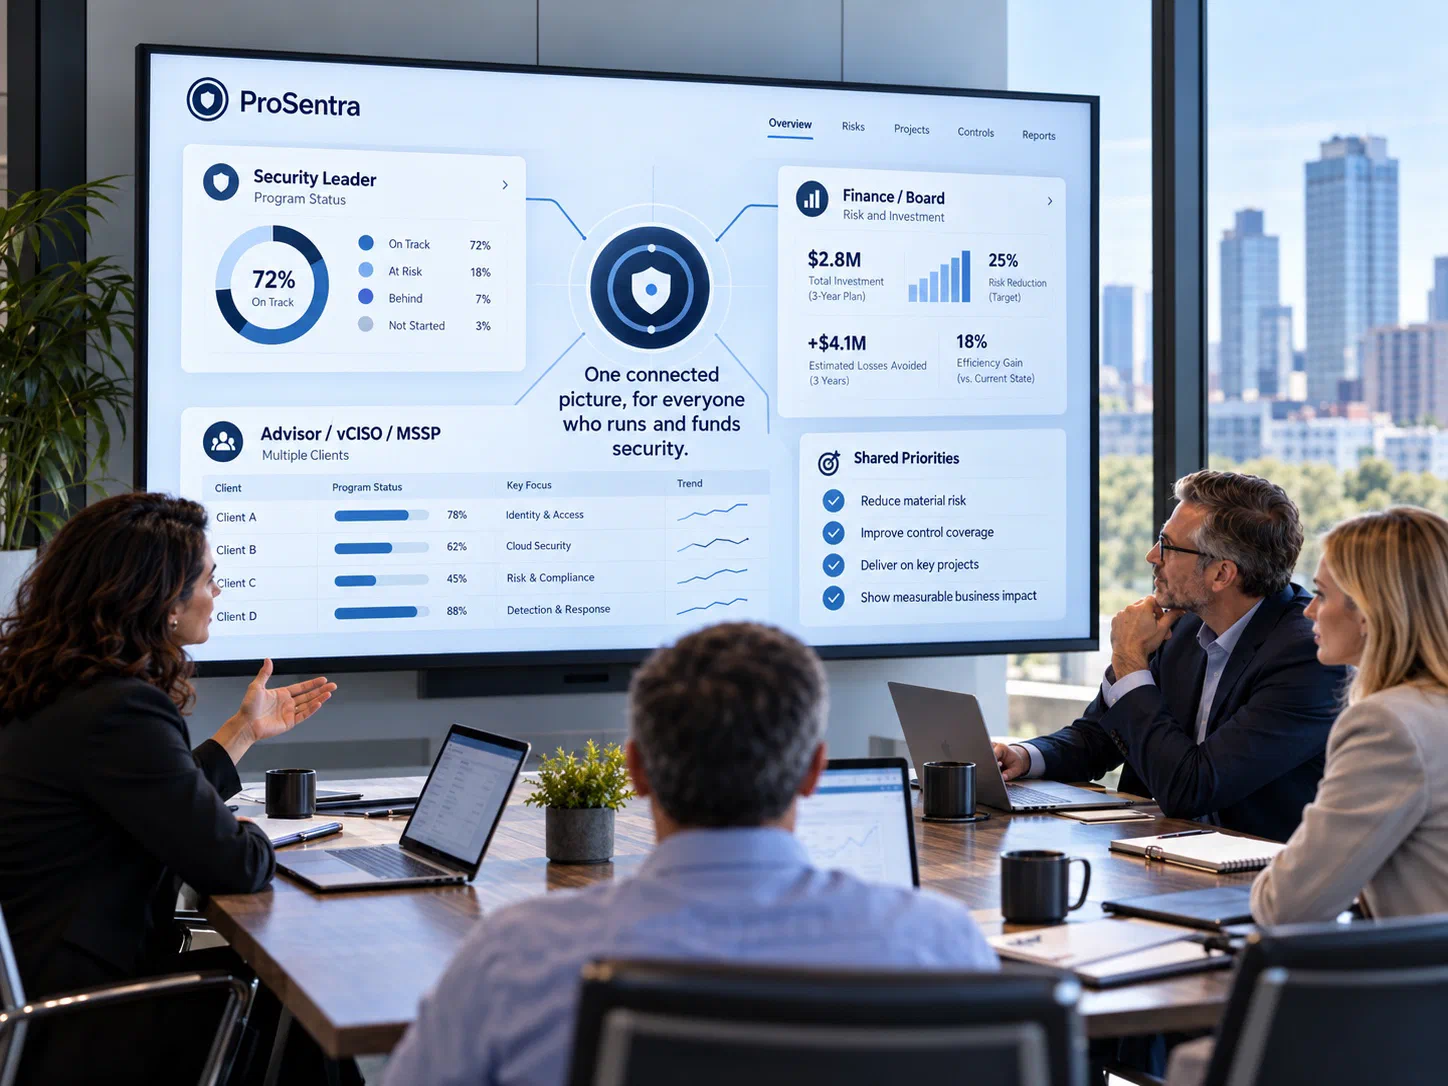
This fall has been busy. Acuity Core and Acuity Essentials are running with customers in local government and consumer products, and we’re in active conversations with security leaders in healthcare, manufacturing, insurance and life sciences, along with MSSPs and advisory firms who assess clients for a living.
Those conversations keep landing on the same few problems. Here’s what we’re hearing, and what we’ve built in response.
What security leaders are telling us
“I can’t see the whole program at once.” Controls are in one spreadsheet, tools in another, the threat picture in a slide deck and the budget somewhere else. Every board meeting starts with rebuilding the picture by hand.
“The assessment is stale the week it’s delivered.” Most leaders have a recent assessment. Few have one that’s connected to the work that followed, so nobody can say what moved.
“I have to defend the budget with activity.” Leadership asks what the money bought. Ticket counts and task lists don’t answer that.
That’s exactly what Acuity Core is for. It connects controls, threats, tools, people and budget, so a security leader can see what reduces risk, what it costs and what to do next, and measure progress against a baseline instead of a feeling.
What MSSPs and advisors are telling us
“Every new client brings the same manual work back.” A fresh spreadsheet, a stack of policy PDFs and weeks of interviews, with quality that depends on who ran it.
“Clients see invoices, not progress.” Between engagements, the value of the work goes quiet, and renewals depend on proving the program moved.
Acuity Essentials gives a practice one repeatable method across every client: documents-first assessments against NIST CSF 2.0 or CIS Controls v8.1, answers checked against the evidence, threat coverage for the groups that target each client’s industry, and a prioritized roadmap, with a portal each client can log into.
New: Solutions pages for each role
We’ve put what we hear from each audience into its own page:
- For Security Leaders: see your entire program at once.
- For MSPs & Advisors: every client assessment, done once and done right.
- For CFOs & Boards: know what your security budget buys.
The last one is written for the people who fund the program. If you’re a CISO, it’s a page you can send to your CFO.
New: the free Security Program Benchmark
Not everyone is ready for a conversation, so we built a way to start on your own. The Security Program Benchmark is fifteen questions covering all six NIST CSF 2.0 functions. It takes about five minutes and needs no login. You see your result on screen right away, against your industry’s typical and target levels, and the full report, with the blind spots you didn’t know to look for, arrives by email.
Let’s talk
We built Acuity because we’ve sat in the CISO’s chair and had the same problems. If any of this sounds familiar, from your own program or your clients’, talk with a founder. We’d like to hear what you’re seeing.