Fractional / V-CISO Services
Strategic security leadership on demand, sized to your organisation.
- Security Program Leadership
- Board & Executive Reporting
Threat-Informed Cybersecurity
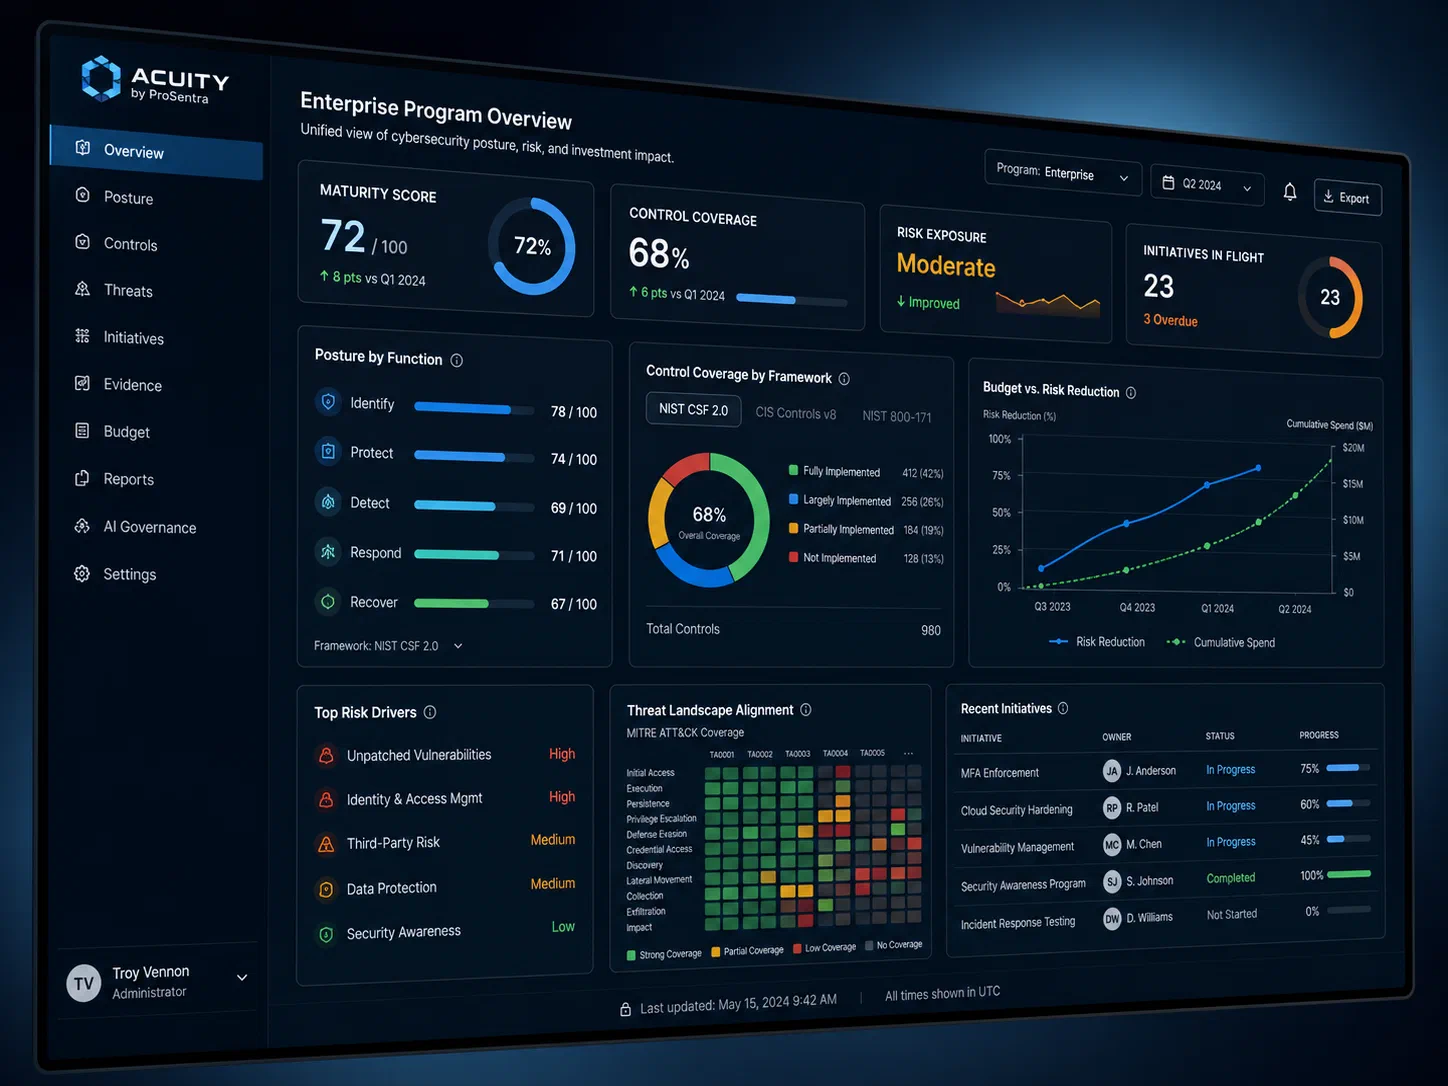
Acuity gives cyber leaders a single system to run their cybersecurity program: assess maturity against NIST CSF, CIS Controls, or NIST 800-171 (CMMC 2.0), prioritize effort, execute with evidence, and measure real progress — while modeling security spend against outcomes. Stop defending budgets with activity metrics and start showing a clear line of sight from investment to risk reduction.
Platform Capabilities
Acuity connects control maturity, tool coverage, threats, people, and budget into one living view — then turns recommendations into tracked work with evidence behind it.
Score controls against your chosen framework and manage the supporting narrative in one place, so the assessment stays current instead of going stale.
See which tools actually cover the techniques your adversaries use, and where you are paying for overlap that buys no additional risk reduction.
Every recommendation carries a priority and a cost, so the roadmap conversation starts from trade-offs rather than a wish list.
Turn recommendations into owned initiatives and tasks, capturing evidence as the work is completed rather than reconstructing it at audit time.
Govern the program on your cadence — quarterly, annual, or continuous — with feedback that updates maturity and coverage scores as work lands.
One view for executives, cyber leaders, and operational teams, with reporting the board can follow from dollar spent to risk reduced.
The Acuity Platform
Acuity is built for CISOs, security directors, and GRC leaders who are tired of running their programs through annual assessments, spreadsheets, and disconnected tools. Whether you need a clear picture of your current maturity or a complete system to run the whole program, Acuity meets you where you are.
Acuity Core
The complete cybersecurity program operating system. Core gives you a closed loop to continuously assess, prioritize, execute, and measure — connecting controls, tools, threats, people, and budget into one living view.
Acuity Essentials
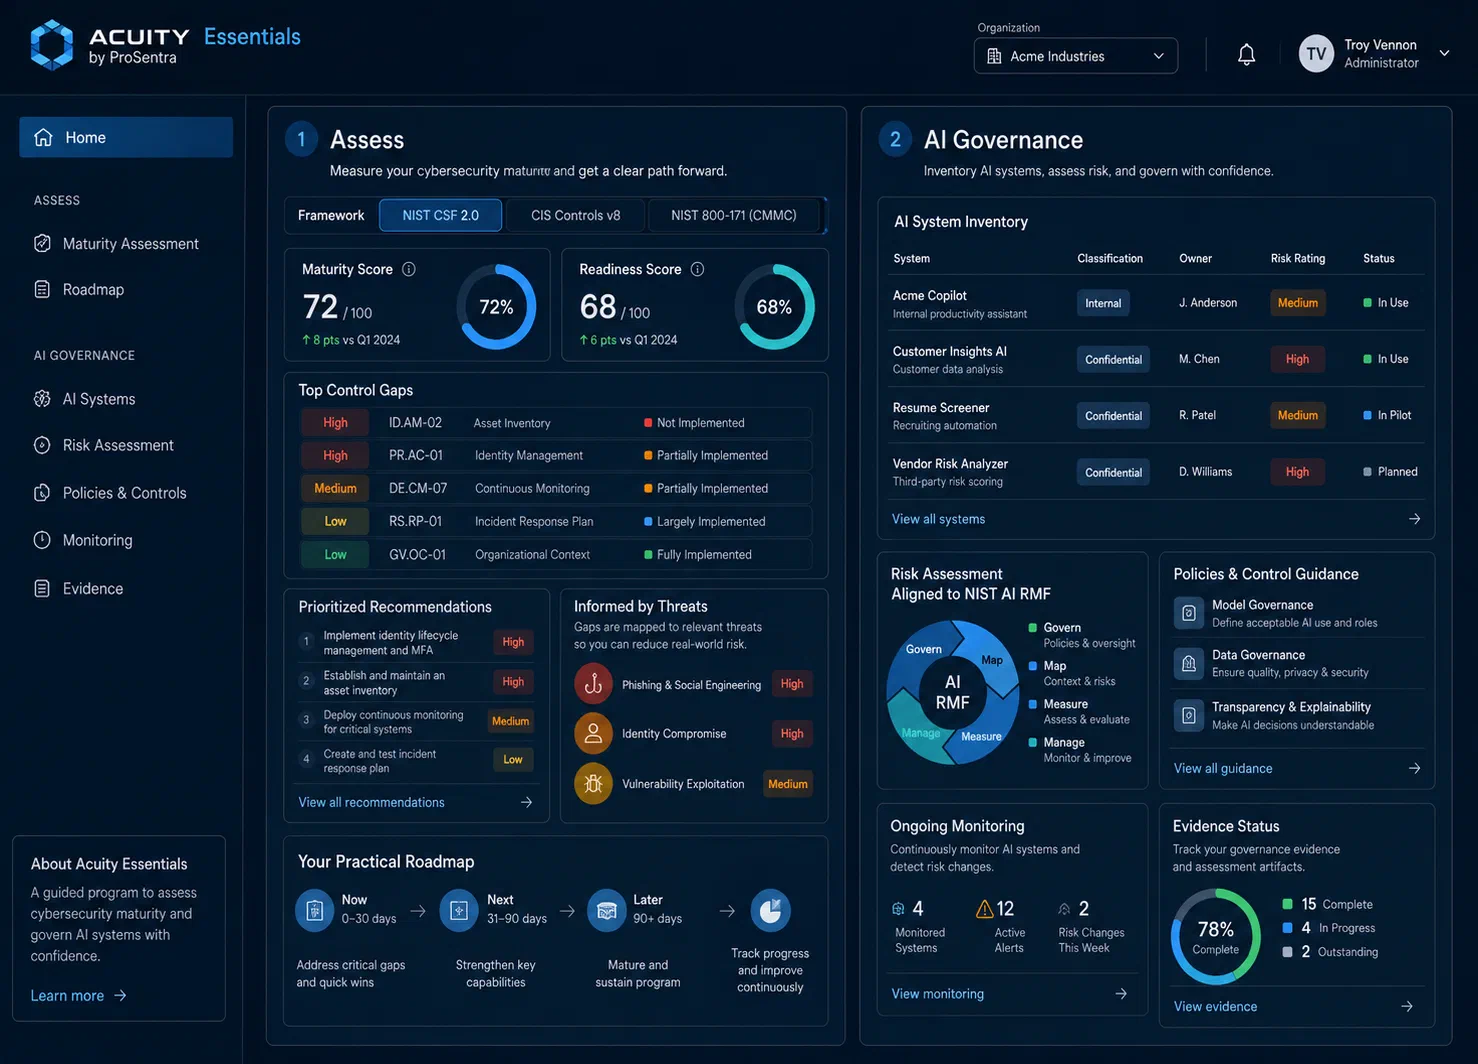
An evidence-backed cybersecurity maturity assessment against the NIST Cybersecurity Framework (CSF 2.0), CIS Controls, or NIST 800-171 (CMMC 2.0), plus AI Governance against the NIST AI RMF — for teams that need accurate scoring, clear priorities, and a ready-to-implement cybersecurity roadmap without standing up the full operating model on day one.
Industry Solutions
Acuity weights your priorities by the threat groups that actually target your industry, and pre-fills maturity targets from industry benchmarks. ProSentra brings that lens to the security program decisions each sector faces.
Assess and prioritize the program protecting industrial control systems, SCADA networks, and operational technology, against the threats that target manufacturers.
Assess the controls protecting patient data, medical devices, and healthcare infrastructure, prioritized by the threats that target healthcare.
Measure how well your controls stand up to the advanced threats that target financial institutions, and show regulators and the board provable progress.
Framework-driven maturity assessment for public sector programs, prioritized by the threats that target government, including NIST 800-171 (CMMC 2.0).
Assess the controls behind point-of-sale security, customer data protection, and e-commerce security, prioritized by the threats that target retail.
Show clients evidence that the controls safeguarding their data, your engagement systems, and the trust your practice runs on are working.
Consulting Services
Comprehensive consulting and managed services to complement our platform capabilities, from fractional leadership through policy, compliance, and engineering support.
Strategic security leadership on demand, sized to your organisation.
Cybersecurity program maturity assessment with budget optimization and roadmap.
Cyber Threat Intelligence program maturity assessment and tooling review.
Comprehensive policy development to strengthen your governance framework.
Insights
Perspectives on threat-informed security, budget strategy, and cyber risk.
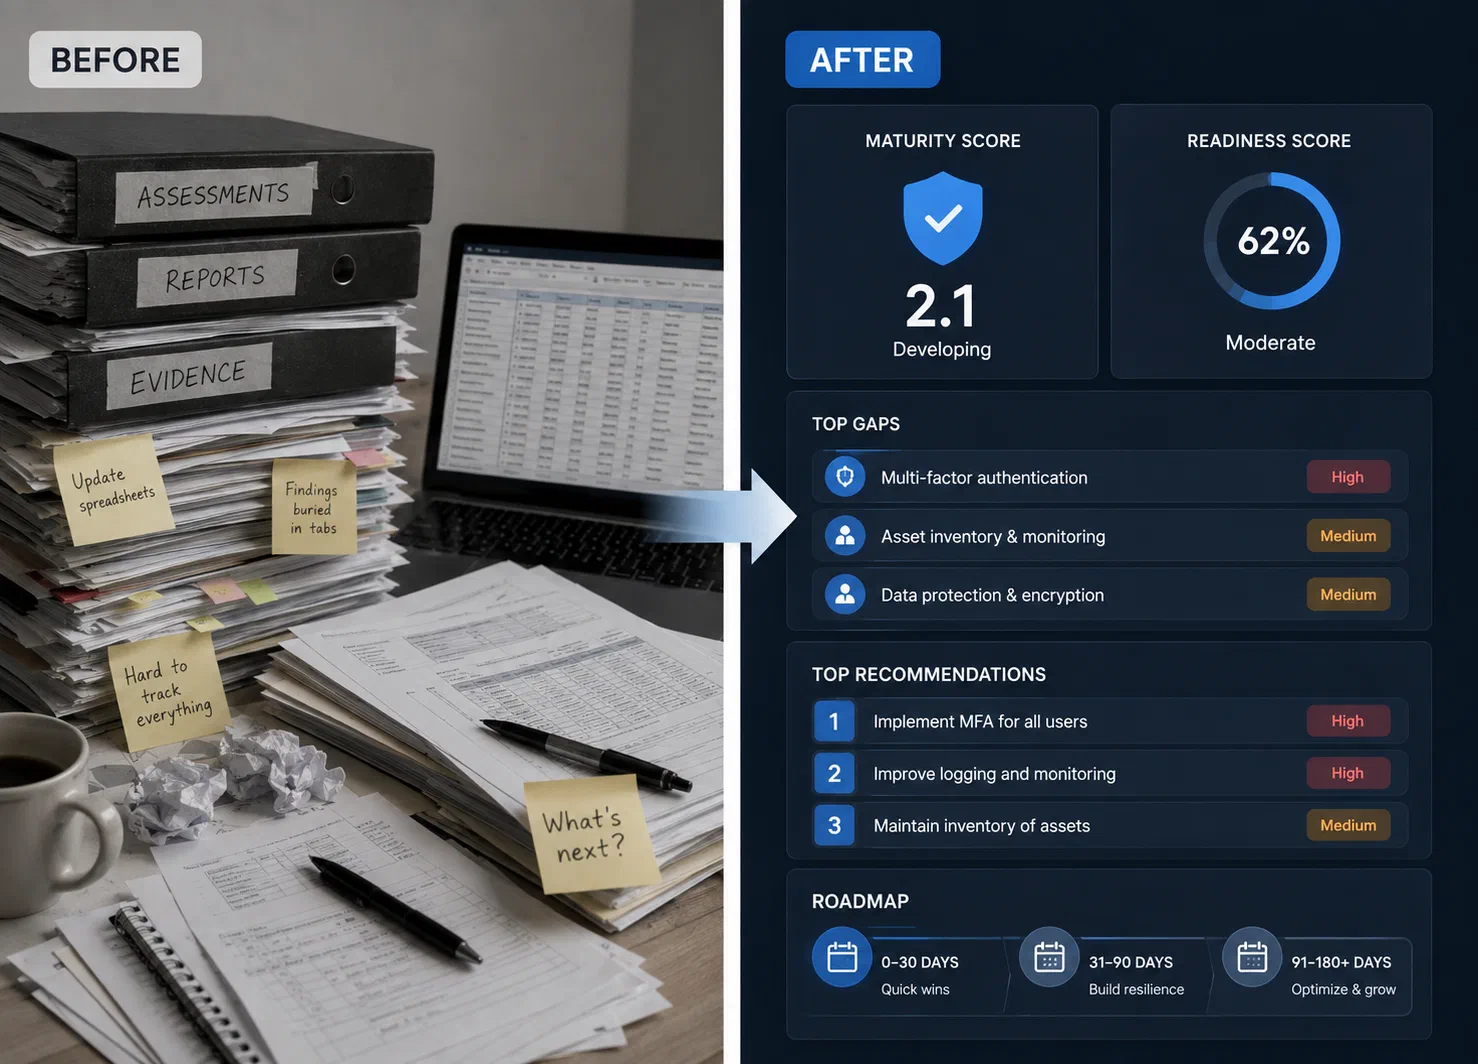
A cybersecurity maturity assessment should tell you where your program stands, which gaps matter against real threats, and what to fix next. Here's how to run one with NIST CSF 2.0.
Acuity Essentials now takes an MSSP from a client's documents to evidence-checked maturity scores, threat coverage, gaps and a roadmap, across every client from one platform.
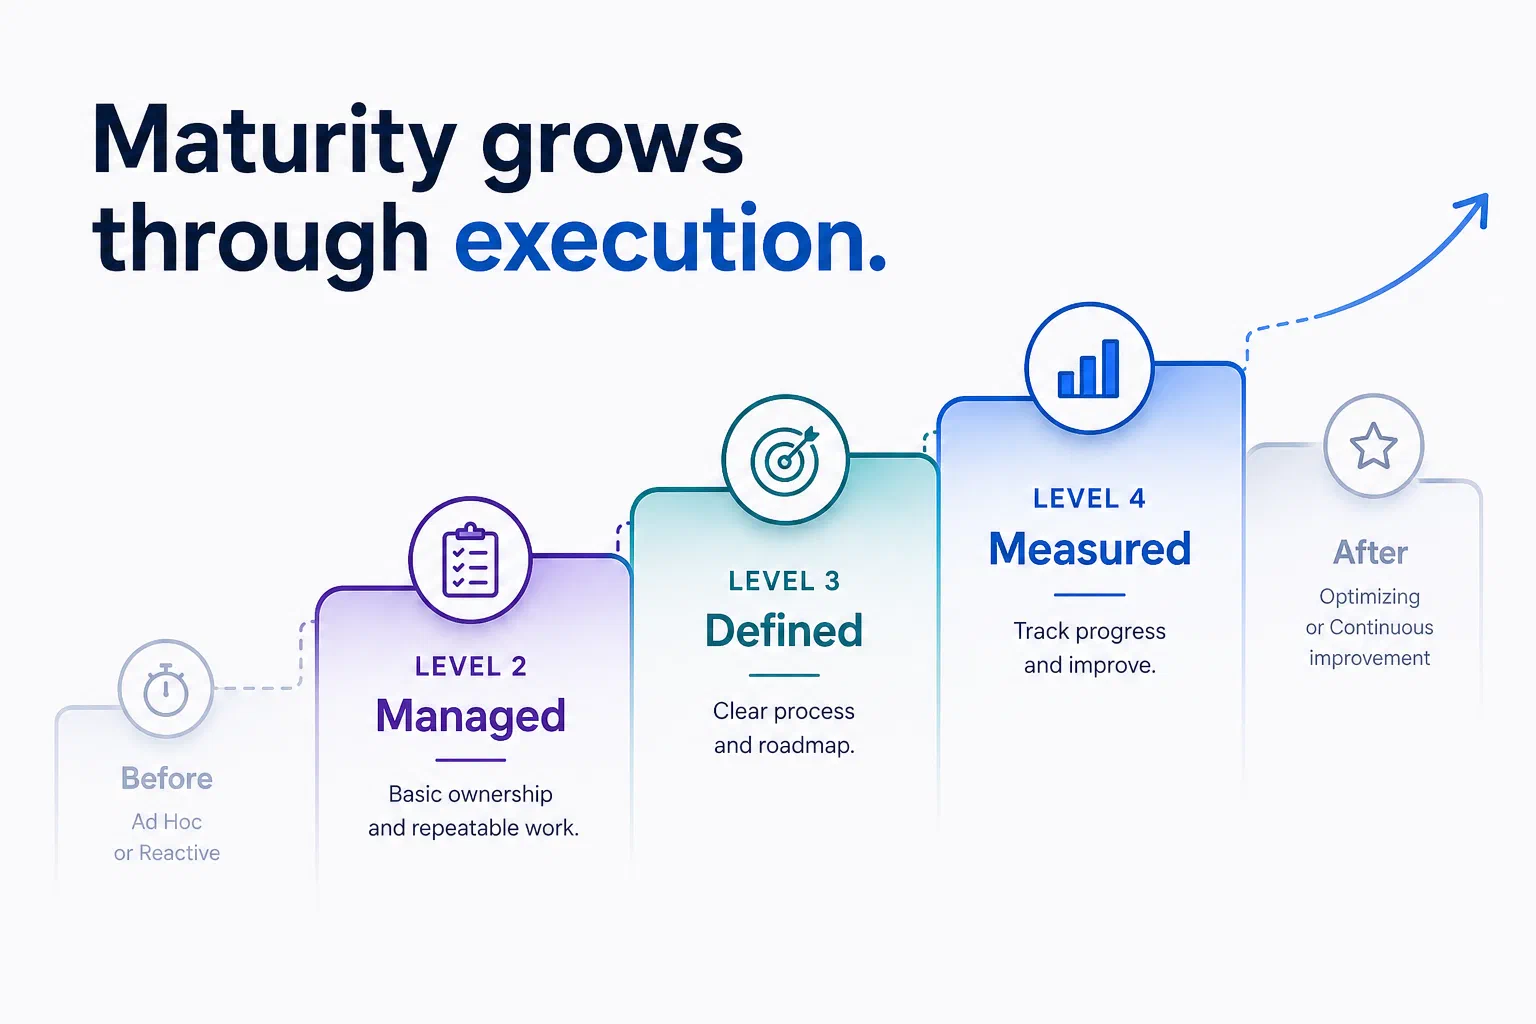
No program has ever matured because someone scored it. Maturity levels describe the work a program can reliably execute — which means the only way up is through execution.
See how Acuity gives security leaders continuous visibility, clearer priorities, and measurable progress — without starting over every year.